Your machine
Real code + secrets
Your engineers paste credentials, API keys and customer data into AI tools every day. Pretense swaps them for stand-ins before they leave the laptop.
 Deploy in 30 seconds
 No credit card required
 Works with your AI tools
Works with any tool that accepts a custom API base URL. Verified end to end with Claude Code, Gemini and Cursor.
Samsung engineers leaked proprietary code to ChatGPT three times in under a month (2023).
This is the part nobody says out loud. Your developers are already using AI every single day, and the security tools you bought were built for a different problem. They watch email and file uploads. They were never built for a senior engineer opening Claude at 2am to fix a release.
The industry spent two decades building walls around the front door. The code walked out through a browser tab.
[09:14:02] → OUT ChatGPT
api_key=sk-prod-7f3a…
[11:42:55] → OUT Claude
patient_ssn=412-55-0199
[14:07:31] → OUT Copilot
// full auth/service.py
[23:58:10] → OUT ChatGPT
db_pass=Pr0d!9x2k
This is not a future risk. IBM put numbers on it this year.
+$670K
added to a breach when staff use AI tools nobody approved
IBM Cost of a Data Breach 2025
1 in 5
breaches now involve one of those unapproved AI tools
IBM Cost of a Data Breach 2025
97%
of AI-related breaches happened with no access controls in place
IBM Cost of a Data Breach 2025
Pretense sits between your developer and the AI, like a proxy on the machine. When code goes out, it finds the sensitive parts and swaps them for stand-ins. The AI does its work on the safe version. When the answer comes back, Pretense puts your code names back in place. Secrets and PII stay as stand-ins and are never put back.
The developer writes code the way they always have. The AI answers the way it always has. The passwords, the patient records, the real names in your code: none of them ever leave the laptop.
Real code + secrets
Swaps secrets for stand-ins
Sees only stand-ins
← code names restored in the reply; secrets and PII stay as stand-ins
Security stops being a thing you bolt on after the fact. It becomes part of the conversation with the AI itself.
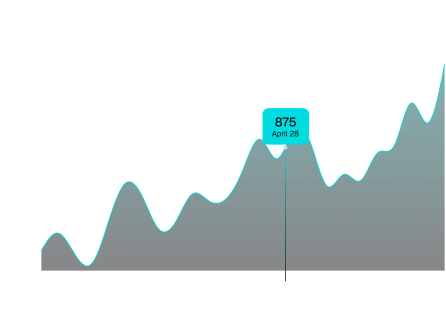
Visualize Code Protection trends over time and understand how AI interactions impact your codebase.
 Real-time Code Protection trends and growth
Identify spikes and unusual activity
Filter by time range and usage patterns
10:55:10 | [SUCCESS] | API key mutated |
|---|---|---|
API key mutated | ||
frontend-web by Emily Tran | src/users/service.py | |
src/users/service.py | ||
10:54:22 | [BLOCKED] | Request blocked: unrecognized secret |
|---|---|---|
Request blocked: unrecognized secret | ||
backend-service by John Doe | src/db/connect.py | |
src/db/connect.py | ||
10:53:55 | [PROTECTED] | SSN mutated |
|---|---|---|
SSN mutated | ||
frontend-web by Emily Tran | src/users/service.py | |
src/users/service.py | ||
10:52:46 | [SUCCESS] | Email address mutated |
|---|---|---|
Email address mutated | ||
frontend-web by Emily Tran | src/users/service.py | |
src/users/service.py | ||
Monitor live Code Protection across your system with instant updates and status visibility.
Real-time stream of Code Protection activity
Status indicators (Success, Blocked, Mutated)
Track user, repo, and file-level activity
Total Code Protection | |
|---|---|
1542 | vs Apr 10- Apr 18 |
Top user | |
|---|---|
 Jimmy Malhan | 28,164 Protects |
Most active repo | |
|---|---|
| 5,593 Protects |
Total Code Protection | |
|---|---|
Scan Proxy | 1120 (73%) 422 (27%) |
Understand key metrics, top contributors, and overall Code Protection activity in one place with better clarity.
Total Code Protection and growth trends over time
Top users and most active repositories overall
Action breakdown & usage analytics across teams
Other tools redact or block the sensitive parts. That deletes the context the AI needs, and the answers get worse with every prompt. Pretense swaps instead of deletes, so the AI never knows anything is missing.
Redact or block — the old way
The sensitive fields are stripped out before the prompt is sent. The model loses the thread and starts guessing.
# what the AI receives
patient = [REDACTED]
ssn =
record = [REMOVED]
 Over a few prompts the accuracy keeps slipping.
Mutation — the Pretense way
The values are swapped for realistic stand-ins on your machine. The AI works normally. Pretense reverts them in the response.
# what the AI receives
patient = "alpha_record"
ssn = "BETA-4471-XX"
record = "mrn_beta_009"
Full accuracy, same speed, and the values that matter never leave the machine.
No procurement process. No rebuilding your stack. Four steps and you are protected.
One command. Works on macOS and Linux.
$ curl -fsSL https://www.pretense.ai/install.sh | sh
Name your team so activity and access stay in one place.
This connects Pretense to the AI tools you already use.
Sensitive data gets swapped automatically before it reaches any model.
That is the whole setup. From install to first protected prompt is about 30 seconds.
Feature | Pretense | Traditional DLP | No Protection |
|---|---|---|---|
Code Protection (preserves AI context) |
|
|
|
Deploys in 30 seconds |
|
| - |
Works offline (local-first) |
|
|
|
Multi-provider (Claude + GPT + Gemini) |
|
| - |
Audit trail with SOC 2 / HIPAA policy presets |
|
|
|
Starting at $0/month |
|
|
|
Perfect for getting started with code protection

10,000 code protections / 7 days
Up to 3 seats
7-day log history
 100,000 code protections / 7 days
More than 3 seats
Usage CSV export
Priority support
Built for growing teams that need more power and flexibility

100,000 code protections / 7 days
1–100 seats
30-day log history
Priority email support
Usage dashboard & CSV export
Dedicated support & CSM
For large organizations with advanced security needs.
Everything in Startup
50 seats minimum, up to 100
Dedicated support & CSM
SLA & uptime guarantee
SAML / SSO (Coming Soon)

Secrets never leave your system unmasked

Built for secure workflows

Works with your existing tools

Cancel anytime seamlessly
Here's everything you need to know before getting started.
Pretense sits between your developers and the AI tools they use, like a proxy on the machine. Before any code or prompt reaches an LLM, it finds the sensitive parts and swaps them for realistic stand-ins. The AI works on the safe version, and when the response comes back, Pretense restores your code names. Secrets and PII stay as stand-ins and are never put back into the reply. Your real secrets and code names never leave the machine.
However you like to start, there's a way in.
Ready to evaluate
Walk through compliance coverage and audit trails with the team.
Want to try it
Install it on your own machine in 30 seconds. No credit card.
Just looking
Watch a 2-minute walkthrough of mutation in a live codebase.

 pretense
